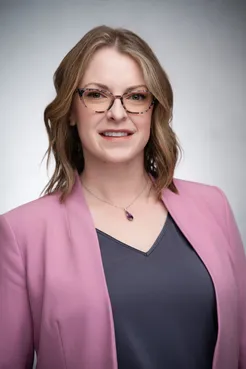
 Photo: Michael Roberts / ISC2 Security Congress 2025
// Virtual CISO
Security decisions
you can defend.
vCISO services for community banks, fintech, and SaaS companies. FFIEC exam prep, SOC 2 readiness, and board reporting, from someone who has sat in the seat.
// Credentials
// Services
Cybersecurity services, sized to your stage.
Virtual CISO, FFIEC exam prep, SOC 2 compliance, and post-incident advisory for community banks, fintech, and SaaS companies.
// Frameworks
What security frameworks does Vaughn Cyber Group work with?
FFIEC, GLBA, NIST CSF, SOC 2, PCI DSS, HIPAA, and GDPR. Security programs built around standards that work, not ones that are trendy.
// Why VCG
Why work with me?
I've done this before. At scale. In environments where getting it wrong isn't an option.
NSA Background
I started my career at the NSA. That's where I learned that security isn't about checking boxes. It's about understanding threats and building defenses that actually work.
Fintech & Banking
CISO at a global payments company and a regional bank. I know what auditors and regulators expect, and how to build programs that pass without the panic.
Compliance That Works
SOC 2, PCI DSS, FFIEC, HIPAA, and beyond. I've been through them all. I build programs that satisfy auditors and actually protect your business. Not one or the other. Both.
Regulatory Exams
FFIEC, state examiners, OCC. Been there.
Vendor Risk
Third-party risk programs that actually work.
Board Reporting
Explaining cyber risk without the jargon.
AI Security
Governance and controls for the AI tools your team already uses, from someone who builds them.
Want to talk about what you're dealing with? No pitch. Just a conversation.
Book a free consult// Resources
Free Resources
Practical security tools and guides. No fluff. Just what you need to get started.
Community Bank Security Kit
Five essential CIS controls for banks, guidance for when you may need outside help, and ready-to-use CIS template.
Startup Security Kit
Essential security controls checklist, incident response template, and the "First 24 Hours Playbook" for startups getting SOC 2 ready.
Virtual CISO FAQ
Everything you need to know about Virtual CISO services: pricing, qualifications, when to hire, and how it works. 15 common questions answered.
// About
Security that makes sense for how you actually work.
Vaughn Cyber Group was founded by Lora Vaughn, a former NSA analyst and two-time CISO with 20+ years of enterprise experience. Our firm bridges the gap between technical security and executive business risk.
With CISO roles at a global payments company and a regional bank, I bring a deep understanding of the security and compliance challenges facing community banks, fintech, and SaaS companies. I know what works and what's just theater. Here's what I don't do: Fear-mongering. Selling you stuff you don't need. Making security so complicated you ignore it.
Here's what I do: Give you straight answers. Build security programs that fit your business. Help community banks, fintech, and SaaS companies get secure without going broke or losing their minds.
Security without the theater.
// FAQ
Frequently Asked Questions
Quick answers to common questions about SOC 2, Virtual CISO services, and working together.
Do I need SOC 2 to close enterprise deals?
How long does SOC 2 certification take?
What's the difference between a Virtual CISO and a consultant?
Do you work with companies outside Birmingham?
// Next step
Need a CISO in your corner?
I'm a one-person firm by design. That means you work directly with me, not a junior consultant. It also means I only take on a few clients at a time. If your timeline matters, let's talk now.
Book a free consult